devagrawal09/jev-review on GitHub
- Stars
- 582
- Forks
- 36
- Language
- TypeScript
- License
- MIT
- Last push
- 17 Sep 2026
Read from GitHub on . Counts change daily.
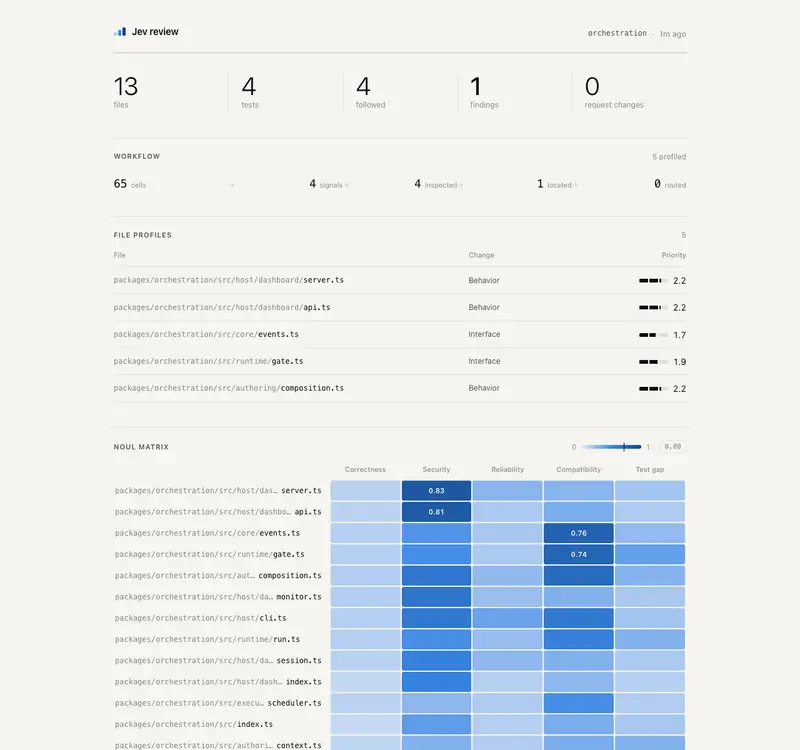
jev-review is a code-review workflow that reviews either the current Git diff or a complete codebase, and shows the result in a local dashboard. devagrawal09 keeps the orchestration in ordinary code and uses Jev only for bounded judgments. It screens for correctness, security, reliability, compatibility, and test coverage, and uses changed or related tests as context when judging test gaps.
The Jev calls run in stages. A noul risk matrix comes first, then choice and score questions build a profile of each file. Further choice questions select the evidence, a concrete diff hunk or source region, and classify the mechanism. A score question rates severity, and a final choice question routes the finding to a reviewer when needed. Thresholds and workflow policy are applied in code, not by the model. The dashboard binds only to 127.0.0.1 and never serves environment files.
The README is upfront about scope: it does not yet integrate compiler diagnostics, static analyzers, repository indexing, or generated explanations, and findings are review prompts, not proof of a defect. It needs Node.js 24 or newer, Git, and a TypeSafe API key.