russfranky/jev-crawlers on GitHub
- Stars
- 1
- Forks
- 1
- Language
- JavaScript
- License
- MIT
- Last push
- 21 Sep 2026
Read from GitHub on . Counts change daily.
PrimitivesNoul
Use casesCompliance verification
Learns a repository's decision norms from its history, then uses Jev to adversarially judge past decisions against those norms, through five Unix-style primitives: seed, expand, judge, verify, report.
Read from GitHub on . Counts change daily.
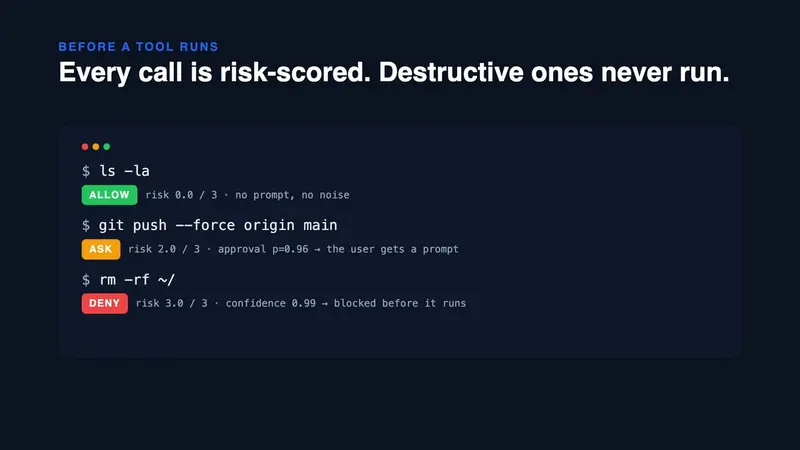
Security hook for coding agents that risk-scores every tool call with session context (deny/ask/allow), flags prompt injection in tool results and checks skills and plugins. Supports Claude Code, Codex, Copilot, Gemini, Cursor, pi, OpenCode and ACP.
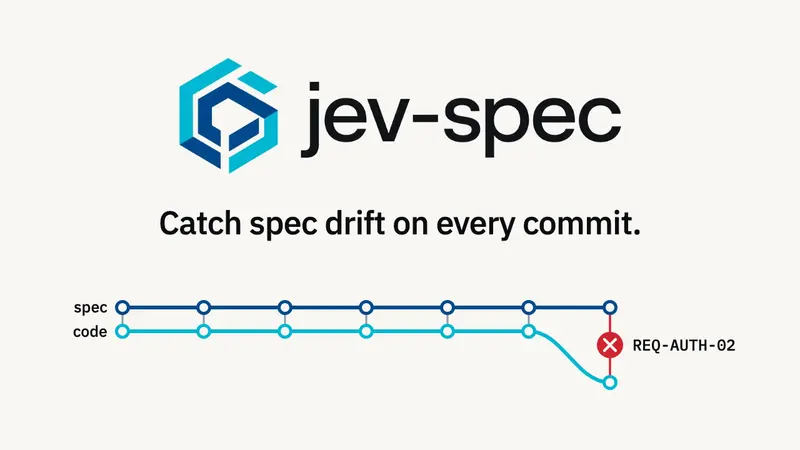
Checks your code against Markdown specs on every commit by asking Jev one focused question per requirement and comparing the returned probability with a threshold you set, failing the build on drift.
Checks an OpenAPI spec for breaking changes hidden in its prose, combining deterministic schema checks with Jev's semantic review.
A configurable GitHub Action that reviews directory submissions and classifies pull requests using only Jev: typed yes/no checks plus one category choice, with code applying the policy and posting one PR comment.
LLM-agnostic guardrails library using Jev to detect prompt injection, jailbreak attempts, PII exposure and credential leaks in one batched request. Not published to PyPI at time of check.
Argues that the purely engineering decisions inside security workflows belong to a typed decision model like Jev rather than a chat model.
 Kostas Tsale (@Kostastsale)OpenRethinking security engineering with Jev (X) on x.com
34k viewsSpeed and cost x200


